Now is the time to ask for the training budget
Now is the time to ask for the training budget
Following recent reflections on effective DPOs, this article looks at another side of the privacy equation: creating the space and support needed to prevent incidents before they happen.
Rather than focusing on workload alone, it explores how privacy teams can use the current spotlight on data protection to make the case for investment in proactive work. From awareness and engagement to training and realistic simulations, the article considers practical ways to strengthen privacy resilience across the organisation.
Making the most of a moment when attention is focused on privacy
5 minute read
Recent events have been a timely reminder that data protection incidents do not always originate from technical vulnerabilities or complex cyber attacks. Sometimes they begin with an individual making a decision, responding to a request, following a process, or simply trying to do their job.
While every incident has its own circumstances, a familiar pattern has emerged. Personal data is not always exposed because someone was careless. It can be the result of persuasion, time pressure, competing priorities, or a request that appears entirely legitimate.
For those of us working in privacy, that poses an important question. If people continue to be one of the main routes through which personal data is compromised, are we investing enough in helping them spot risks, challenge what does not feel right, and know what to do when something seems unusual?
The annual training problem
Most organisations I have worked with require data protection and cyber security training once a year. It sits in the learning portal alongside anti-bribery, health and safety, modern slavery, equality and diversity, and whatever else the year has added. A deadline is set, reminders go out, and completion rates are reported upwards.
Whilst completion rates are useful, they show that the training was done. They tell us very little about whether anyone took something away from it. I suspect most of us have seen, and perhaps been, the person clicking through a module in the gap between meetings so the reminder emails stop. That is no reflection on staff. When everything is mandatory and everything arrives at once, it all starts to blend together.
The attacks in the headlines are not waiting for the annual refresher. A fraudulent request from a convincing domain, or a message from someone who sounds like a colleague or supplier, relies on a moment of trust under time pressure. That is why awareness needs to be reinforced regularly, not just once a year.
Why now is the time to ask
If there has ever been a time for privacy leaders and their teams to ask for more budget, I think it is now. Boards and executive teams have seen these stories. They have seen a share price move on the back of a single push notification, and if your organisation is not already talking about this, I would be surprised. If they are not aware, tell them. The conversation about what a breach costs is no longer theoretical, and that gives privacy teams an opening that may not stay open for long.
My suggestion, however, is not to lead with the fact that the privacy team is stretched. Most organisations already know their teams are busy, and if that alone has not unlocked additional investment, it is unlikely to do so now.
Instead, make the case for what more could be achieved. Additional resources creates the capacity to spend more time on the preventative work we all know matters, including more meaningful engagement with the business, regular awareness activities, in-person training sessions, open Q&A discussions, and realistic simulations that help people recognise and respond to suspicious requests. In other words, ask for the budget to reduce risk, not simply to manage workload. The extra pair of hands will make that possible.
We all learn from experience
Some people learn best by reading, others by doing. Whilst that is true, most of us learn most effectively through experience. Very few people forget the first time they nearly fell for a scam, or the first time they sat in a room trying to work out whether an incident needed to be reported to the ICO within 72 hours.
That is why awareness should be about more than an annual training module. Regular engagement with the business, in-person discussions, Q&A sessions and realistic exercises all help to bring the risks to life.
Simulation gives people the opportunity to gain that experience without the real-world consequences. In practice, it could include:
phishing and social engineering exercises, including requests that appear to come from regulators, law enforcement or senior colleagues
scenario walk-throughs where teams decide whether what they are looking at is a personal data breach
tabletop exercises that take a breach from discovery through containment, risk assessment, notification and communication with customers
short, regular refreshers that reflect current events and emerging threats, rather than relying on a single annual training session
If people have already experienced what it feels like to spot a scam, recognise that something has gone wrong, or manage the first hours of a breach, they are far more likely to respond well when faced with the real thing.
Working with cyber security
This is also an opportunity to work more closely with cyber security colleagues. Many security teams already run phishing simulations. Privacy teams bring an understanding of what personal data is at stake, the regulatory obligations and the impact on individuals. Combining the two creates exercises that feel more relevant to the business and better reflects how incidents unfold in practice.
There is another benefit that is easy to overlook. Privacy teams are often small and stretched, and some are a team of one. A workforce that knows what to look for and feels confident raising concerns tends to escalate issues earlier and with better information. That can make a significant difference in the first hours of an incident, when the privacy team is trying to understand what has happened, assess the risks and decide what action needs to be taken.
A realistic view
Simulation will not suit every organisation or every environment in the same way. Budgets differ, cultures differ, and some sectors will need to think carefully about how realistic an exercise can be. A simulated phishing exercise can damage trust if it feels like a trap, so it should be approached as a learning opportunity, with support, feedback and no blame.
Even so, I still think now is the time to push for that little extra. The consequences of a breach, from customer complaints and regulatory scrutiny to media attention and the pressure placed on the people managing the response, are something no organisation wants to experience. Investing in awareness, engagement and practical exercises is often a far smaller commitment than dealing with the aftermath. Not every organisation will have the capacity to do more with its existing team. Sometimes an extra pair of hands can make all the difference, creating the time and space needed to focus on the preventative work that is so often pushed down the priority list. Whether that support comes from within the business or from outside it, investment in meaningful engagement, training and testing is rarely wasted.
The organisations that navigate incidents best are not necessarily those with the biggest privacy teams. They are more likely to be the ones that have invested in helping their people recognise risks early, raise concerns confidently and respond in a way that feels familiar when it matters most.
Creating the space for proactive privacy work
Awareness, engagement, training and testing all take time. If you're looking to create more capacity within your privacy function, an independent perspective can help identify priorities, opportunities and areas for investment. Additional support can also provide the extra pair of hands needed to deliver awareness activities, strengthen governance and progress the preventative work that too often slips down the priority list. The challenge is rarely knowing what needs to be done. More often, it is finding the time and capacity to do it well.
Next, I'll be looking at ‘Who's Watching the Workplace Watchers?’
Stay in the loop
If you found this useful, subscribe to the Roseline Data Privacy monthly newsletter and never miss out on our practical data privacy insights, updates, and tips delivered straight to your inbox. No noise, just what matters.
What makes a good DPO?
What makes a good DPO?
Recent reporting on the ASOS incident is a timely reminder that effective privacy governance matters long before an incident occurs.
While the facts are still emerging, events like these highlight the importance of ensuring Data Protection Officers have the independence, access and organisational support needed to provide effective advice when it matters most.
The recent article explores a simple question: What makes a good DPO?
Read the article and view the accompanying carousel below.
The real test of a DPO comes when expertise meets organisational reality.
7 minute read
On Tuesday morning, ASOS app users received a push notification that did not come from ASOS. It was addressed to the company’s DPO and IT team, claimed that the sender had “fully compromised the Snowflake instance”, and ended: “Engage with us, or we will leak it.”
At the time this article was drafted, ASOS had confirmed unauthorised activity involving third-party platforms used to communicate with customers and stated that names and contact details may have been exposed. ASOS said it did not believe payment card details or account passwords had been affected. Snowflake also stated that it had found no compromise of its own platform.
The facts are still emerging and I will not speculate about what happened inside ASOS. My thoughts are with the teams working through it, and with the customers wondering what it means for them. Anyone who has managed a serious incident knows how intense those first days are. It is unusual to see a DPO named in the attack itself, and it is a reminder of how much rests on that role when something goes wrong. The DPO is expected to advise quickly, calmly and independently, often on incomplete facts and under real pressure. They can only do that well if they have been properly supported and empowered long before the incident arrives, with clear access to decision-makers, organisational standing, sufficient resources, operational independence, and the backing needed to give difficult advice and have it heard.
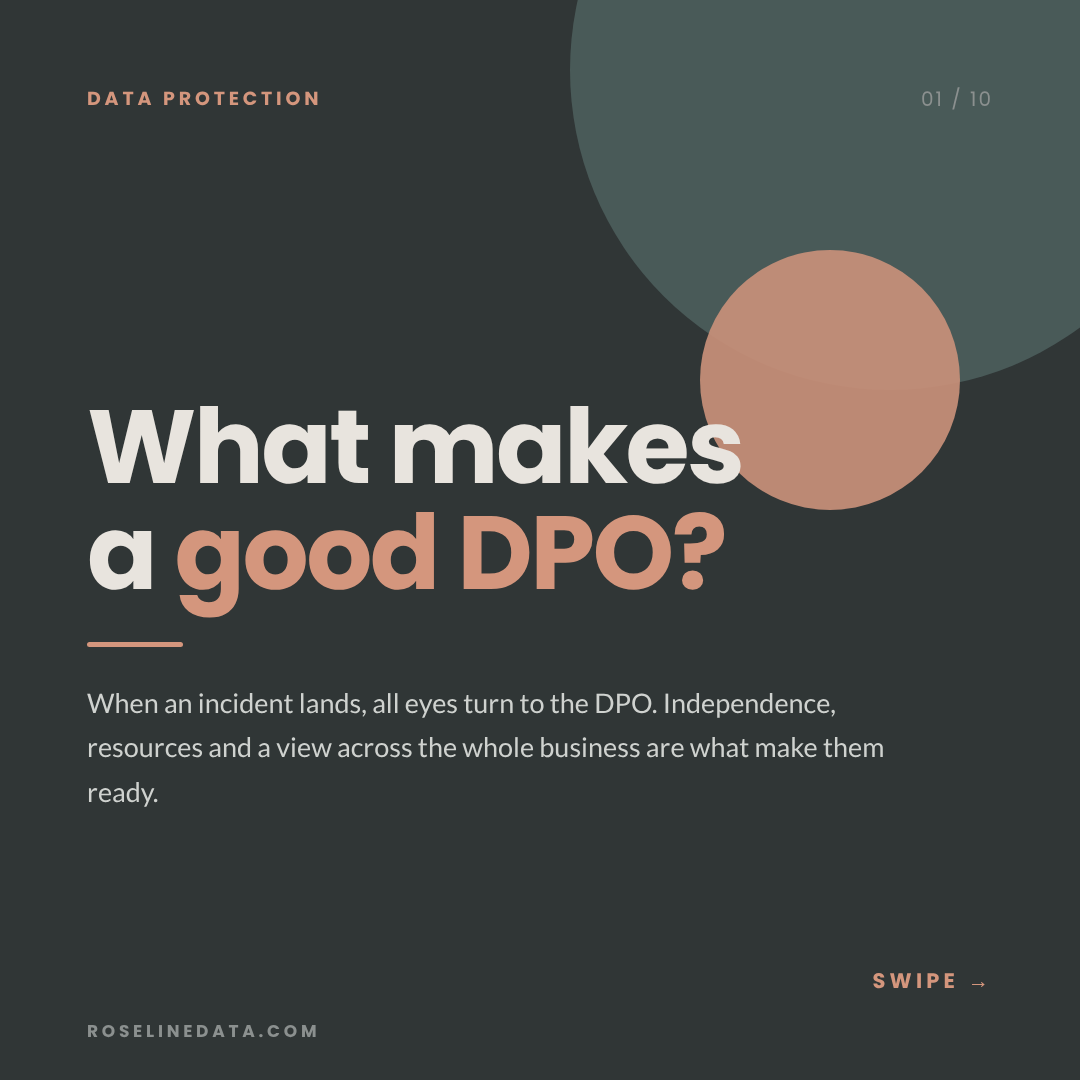
I have put together a short carousel on what makes a good DPO, and this week felt like the right time to share it. None of what follows is about blame. It is about ensuring the person in that seat has the access, support and authority they need to be effective when they are needed most.
The question usually gets answered with a list of qualifications. Expert knowledge of data protection law, familiarity with the sector, a working understanding of the organisation's processing. All of that matters, and none of it is optional. Whilst those things are necessary, they are rarely what determines whether a DPO succeeds. In my experience the difference is made by the conditions the organisation puts around the role.
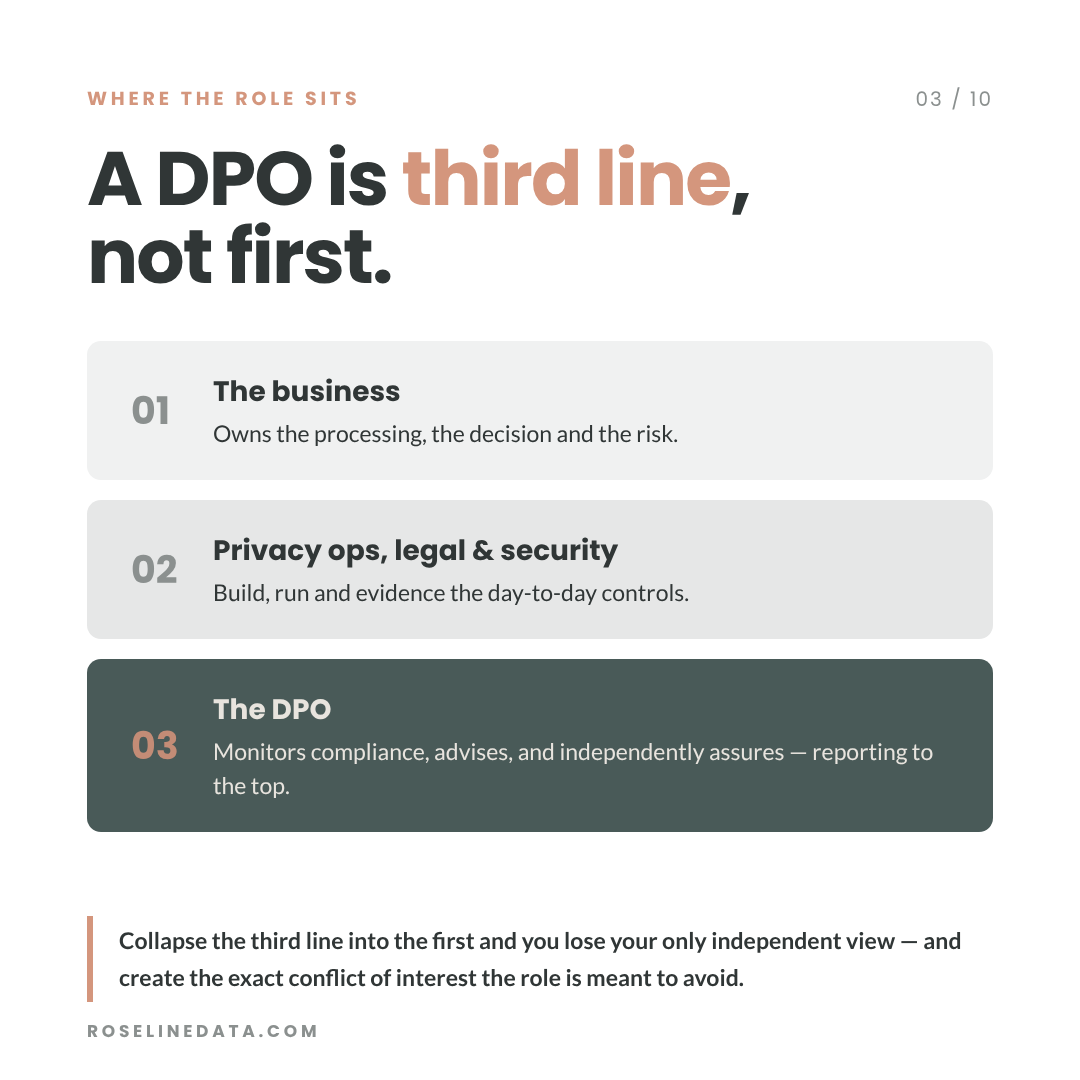
The DPO belongs in the third line of defence
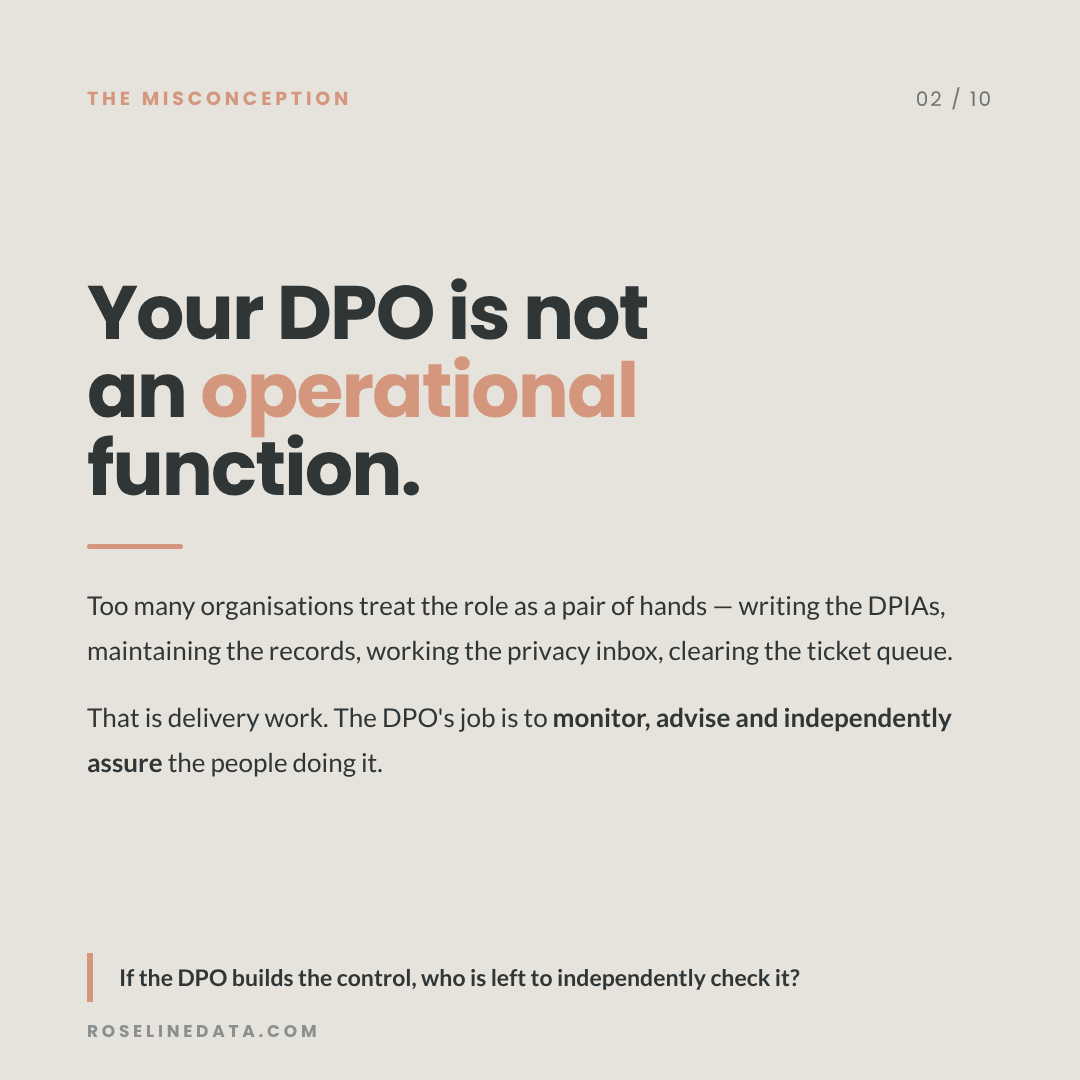
Many organisations treat the DPO as an operational function. The DPO writes the DPIAs, maintains the record of processing, works through the privacy inbox and clears the ticket queue. That is delivery work, and it sits properly in the first and second lines, with the business that owns the risk and the teams that build and run the controls.
Article 39 gives the DPO a different task: to inform, to advise, to monitor compliance and to cooperate with the supervisory authority. That is third line work. It only means something if it is performed independently of the activity being reviewed. If the DPO designs and builds the control, there is nobody left to assess whether the control actually works. Article 38(6) is clear that any other tasks must not give rise to a conflict of interest, and doing the work whilst also assuring it is precisely such a conflict. The person advising on whether to notify the ICO and affected customers should not also be the person whose controls are under review.
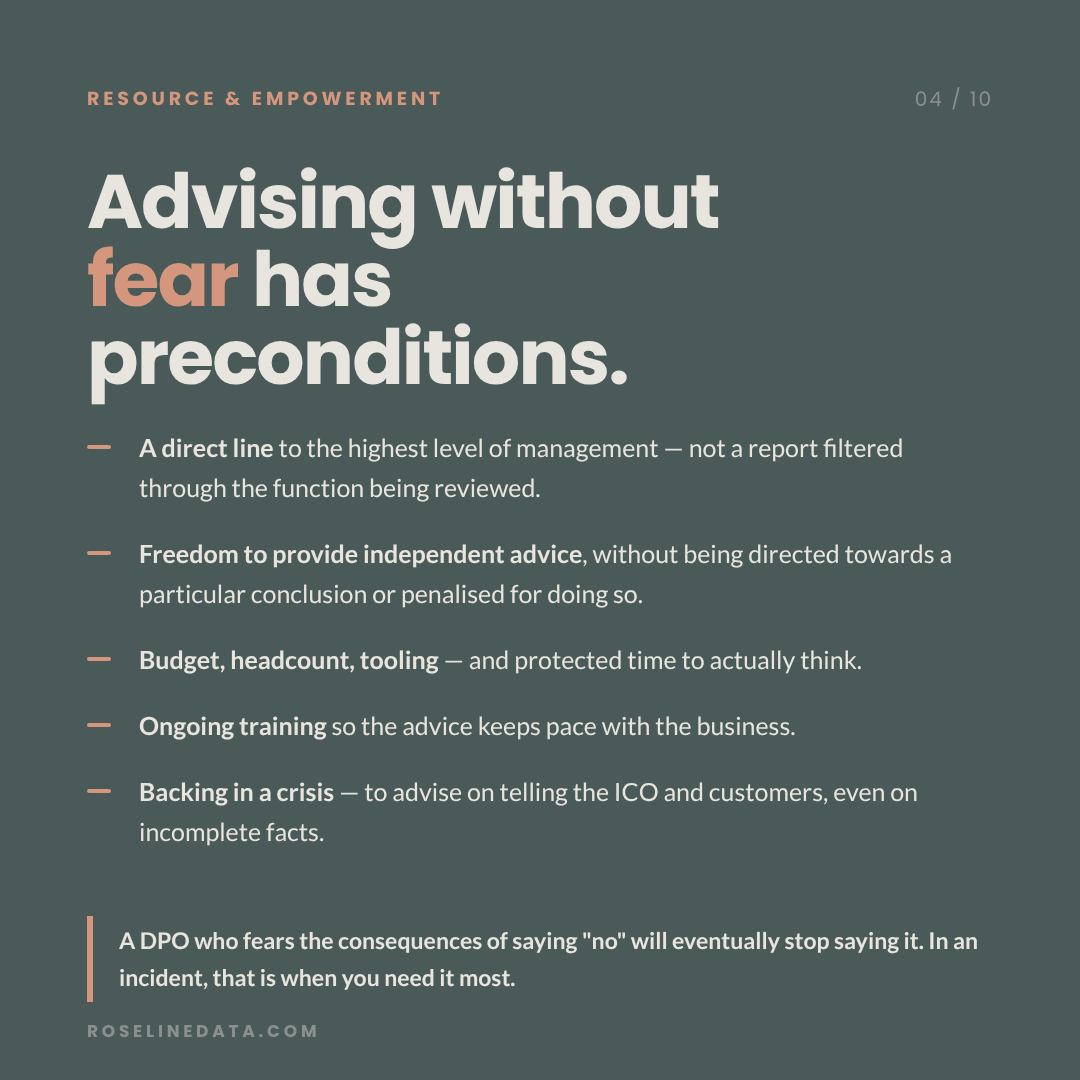
Advice given without fear
Independence is written into the Regulation. Article 38 requires that the DPO receives no instructions regarding the exercise of their tasks, is not dismissed or penalised for performing them, and reports to the highest management level. Article 38(2) requires that the organisation provides the resources necessary to carry out those tasks and to maintain expert knowledge.
In practice, independence is something an organisation grants rather than something a DPO can declare. It looks like a direct reporting line that is not filtered through the function being reviewed. It looks like budget, headcount, tooling, training and protected time. A DPO who is uncertain about the consequences of giving unwelcome advice will, over time, give less of it. That is a quiet risk, and it does not show up on a compliance dashboard. The real test often comes in the first few hours, when a DPO may need to recommend notifying the ICO on incomplete information, or telling customers what has happened and what steps they can take to protect themselves, before the business feels fully ready to do so.
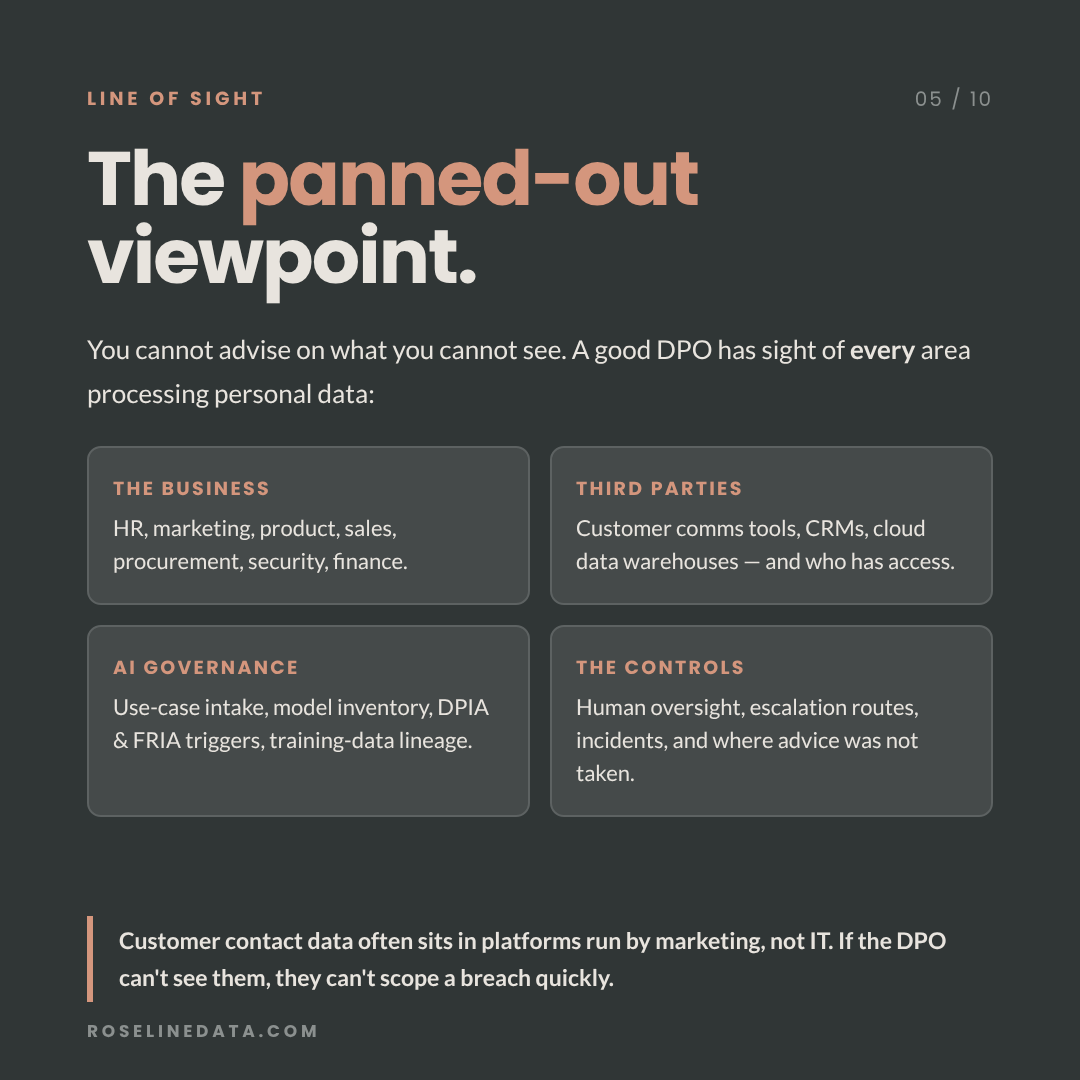
The panned out view
A DPO can only advise on what they can see. That means line of sight across every area of the business processing personal data, including HR, marketing, product, sales, procurement, security, finance and data teams, as well as the third parties acting on the organisation's behalf and the platforms they provide.
The ASOS incident, as reported so far, appears to involve third-party platforms used to communicate with customers. Customer engagement tools, push notification services, CRM systems and cloud data platforms can hold significant volumes of customer data, and responsibility for them may sit across marketing, digital, data and technology functions. If a DPO does not have visibility of which vendors process customer data, what information they hold, and who can access those systems, it becomes far harder to assess risk in advance or help scope and respond to a breach when one occurs.
Where responsibility for AI governance sits with the DPO, the same principle applies. Seeing the completed assessment is not the same as understanding how use cases are identified and approved, how the model inventory is maintained, what triggers a DPIA or fundamental rights impact assessment, where training data comes from, or how human oversight is demonstrated. A DPO reviewing the output of a governance process without visibility of the process itself can offer only limited assurance.
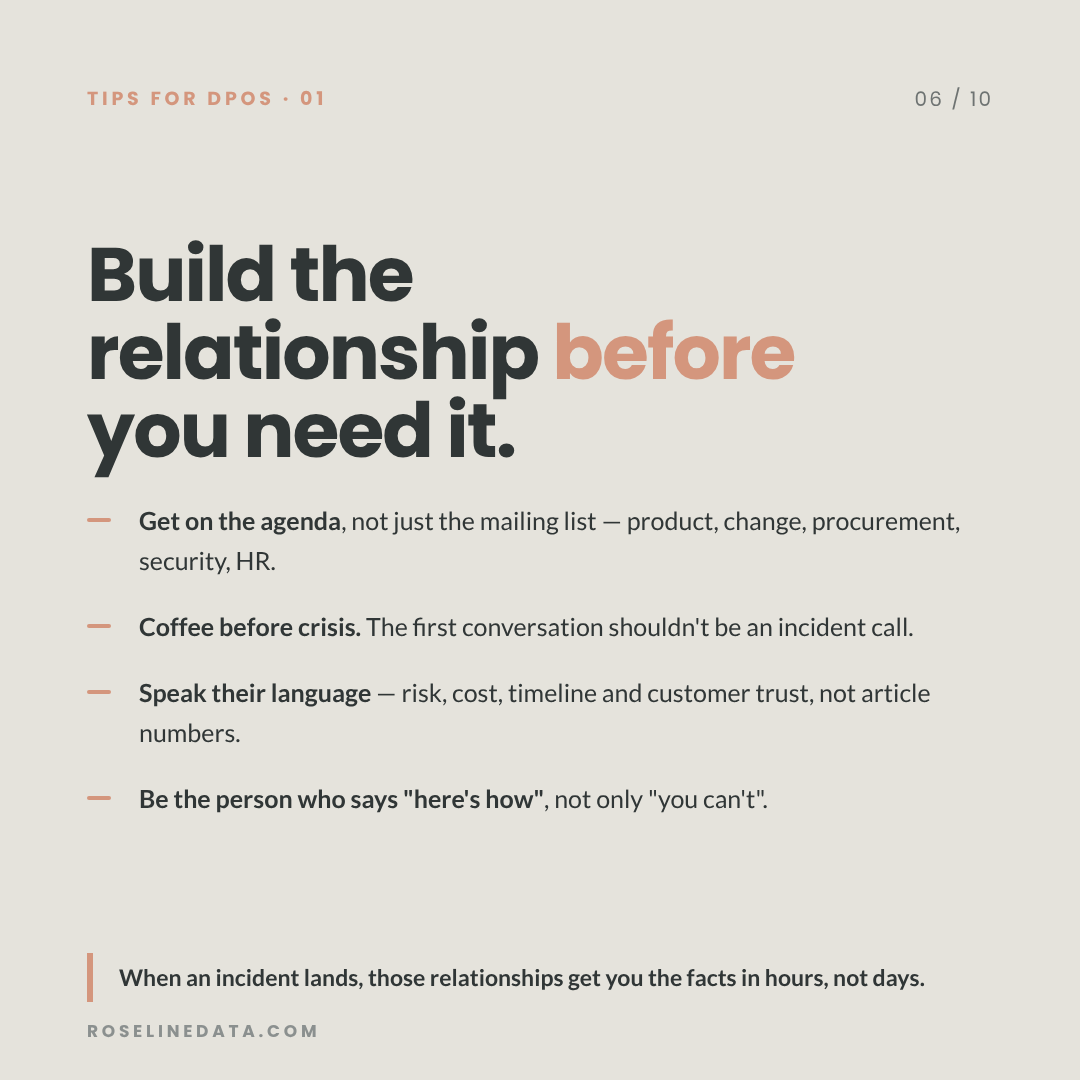
Presence across the organisation matters
An advisory role runs on influence, and influence is built long before it is needed. It helps to be a familiar face around product, change, procurement, security and HR forums rather than simply another name on the mailing list. Building relationships early creates trust and, over time, a group of listening ears when difficult conversations need to happen. The first interaction with a team should not be during an incident or compliance escalation. When an incident does land, those relationships are what get the DPO accurate facts from marketing, security and the vendor in hours rather than days. Advice is also more likely to be acted on when it is expressed in terms the business already understands, such as risk, cost, timelines and customer trust, and when it helps teams find a safe path forward rather than simply pointing out the limits.
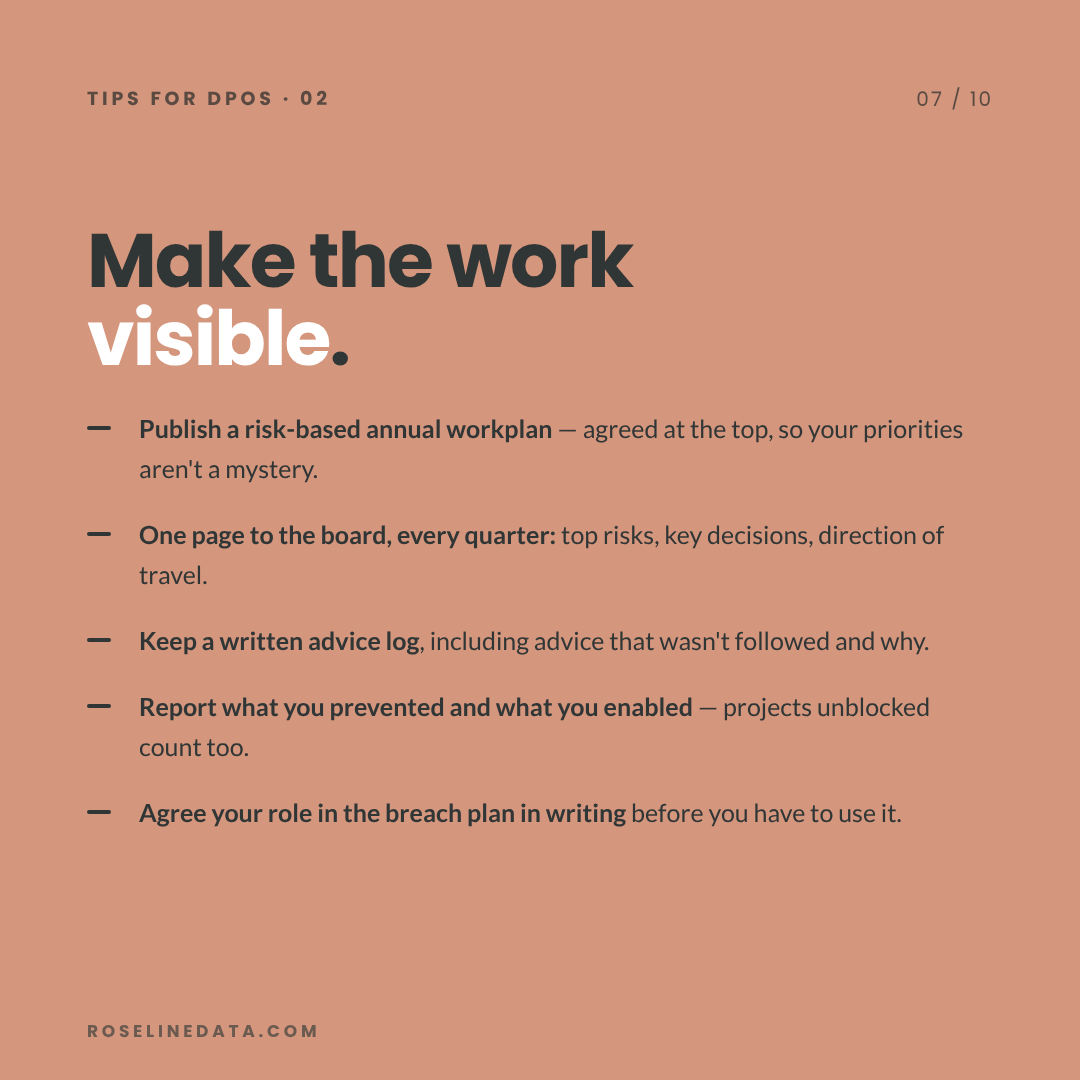
It also helps to make the work itself visible. A risk-based annual workplan, agreed at the highest level, helps the organisation understand the DPO's priorities and the reasons behind them. Regular attendance at team meetings and governance forums provides valuable insight into evolving risks, levels of understanding, and where additional support or training may be needed. It also creates opportunities to gather meaningful data and metrics that demonstrate trends, resource pressures, and the case for further investment in privacy and governance. A short quarterly report to the board helps keep privacy on the agenda throughout the year, not just when an incident occurs. Maintaining a written record of advice given, including advice that was not followed, supports accountability and protects all parties. Just as importantly, the DPO should highlight the good privacy practices being adopted across the organisation, not just the risks, incidents and poor practices that have been identified and addressed.
Empower the role, then assess its impact
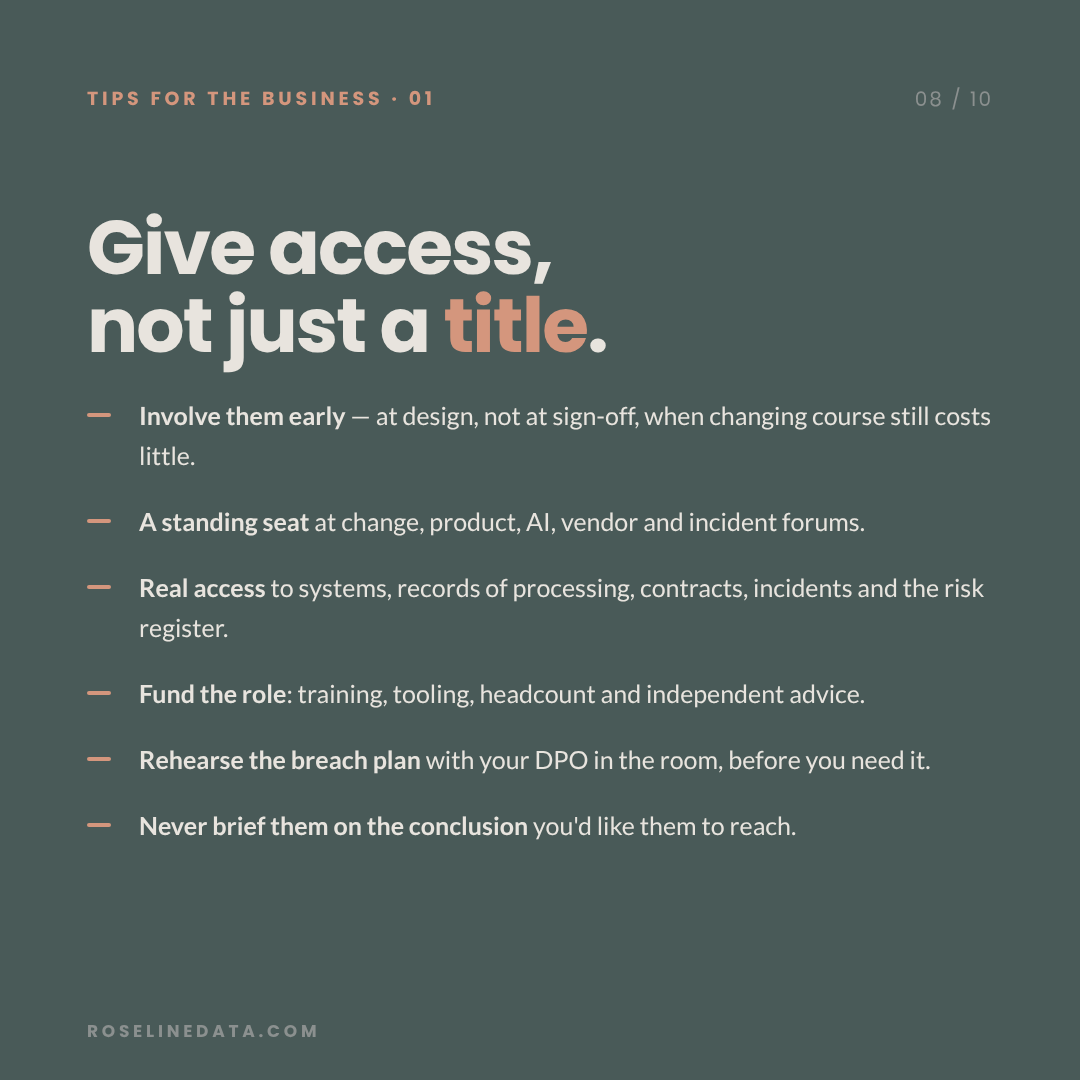
The most effective DPOs are involved early, when ideas are taking shape and changes can still be made quickly and at relatively low cost. A regular seat at change, product, AI and vendor governance forums is often more valuable than any job title. So too is access to the information needed to do the role properly: systems, records of processing activities, contracts, incident logs and the risk register, together with a clearly defined role in the incident response plan and sufficient budget for training, tooling and specialist advice.
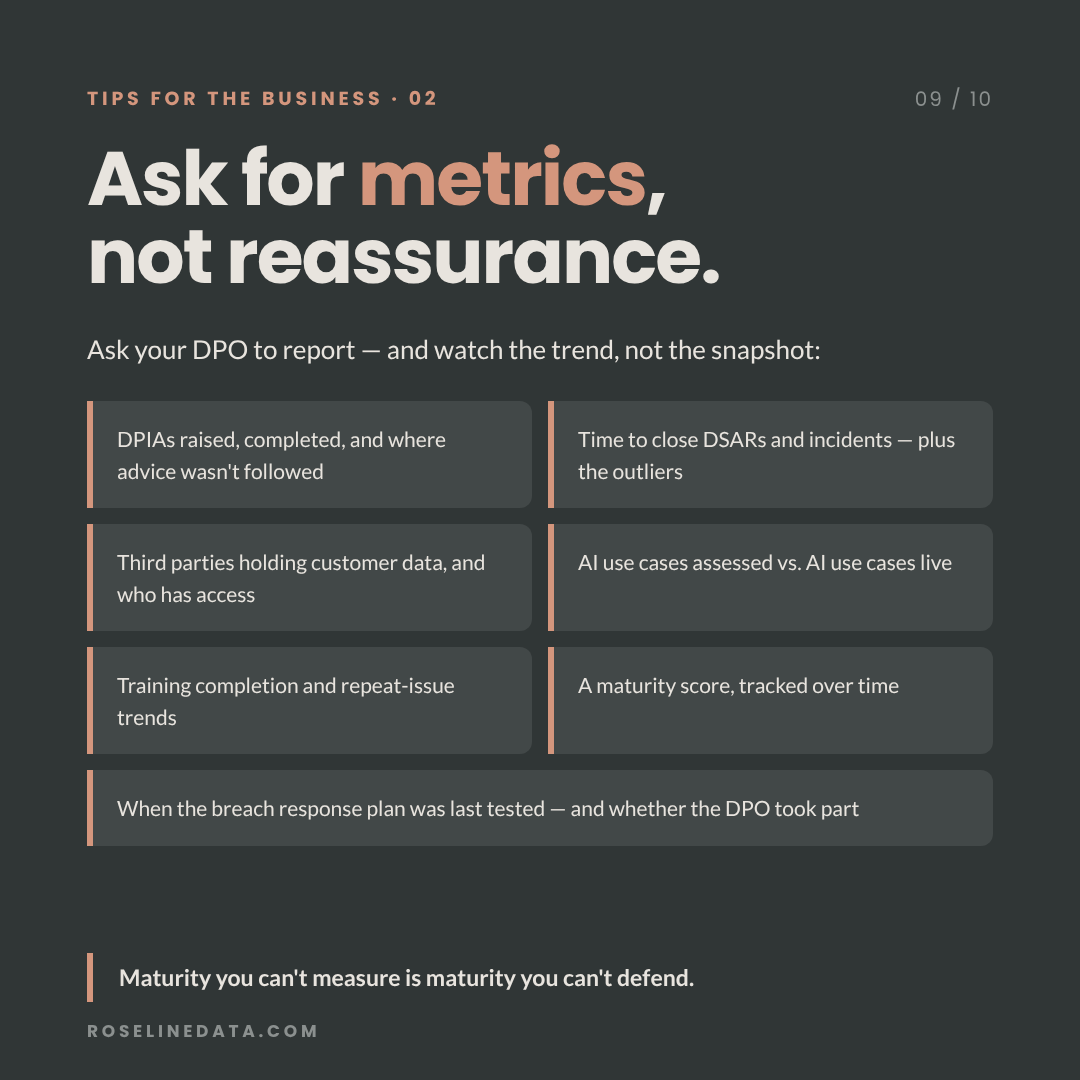
Reporting then becomes important. Rather than focusing on isolated snapshots, organisations should look at trends over time and the direction of travel. Useful metrics for a DPO to report on include:
DPIAs raised and completed, including any occasions where DPO advice was not followed.
Time taken to respond to data subject requests and close incidents, including more complex or higher-risk cases.
Oversight of third-party providers and international data transfers.
AI use cases assessed, compared with those in active use across the organisation.
Training completion rates, recurring themes and repeat issues.
Privacy and governance maturity, tracked over time.
Maturity that is not measured is difficult to demonstrate, whether to a board, a client or a supervisory authority.
In short
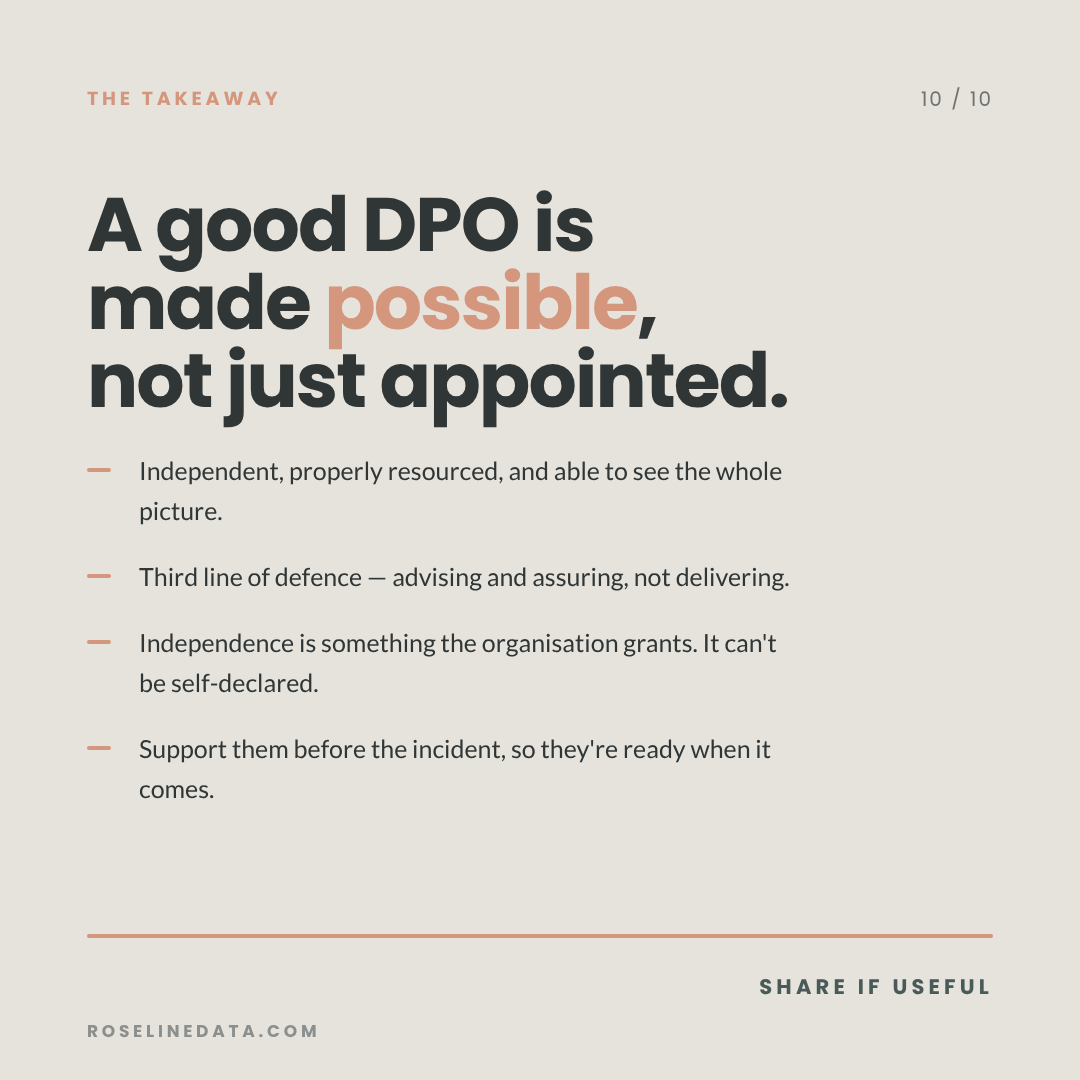
A good DPO is knowledgeable, independent, properly resourced and able to see the whole picture. Three of those four are given by the organisation, and incidents like this week’s are when they are tested, in public and at speed. Get the conditions right and the DPO stops being seen as a barrier to the business and becomes an early warning system for it.
The carousel below brings these points together across ten slides. If you find it useful, please feel free to share it with colleagues.
Is your DPO function set up for success?
A capable DPO can only be effective when the right governance, reporting lines, access and support are in place. If you would like an independent review of your current arrangements, I would be happy to help identify gaps, clarify priorities and suggest practical next steps.
Next, I'll be looking at ‘Now is the time to ask for the training budget’
Stay in the loop
If you found this useful, subscribe to the Roseline Data Privacy monthly newsletter and never miss out on our practical data privacy insights, updates, and tips delivered straight to your inbox. No noise, just what matters.